Privacy and AI compliance for companies that cross borders.
We work out which privacy and AI laws apply to you in every country you serve, what has to change, and in what order. Every requirement is cited to the official text.
Privacy, AI and cyber laws across India, Europe, the Americas, Asia-Pacific, the Middle East and Africa. Fixed fees, agreed before any work starts.
- DPDP Act
- GDPR
- EU AI Act
- NIS2
- Cyber Resilience Act
- DORA
- CERT-In
- UK GDPR
- CCPA / CPRA
- NIST CSF 2.0
- NIST AI RMF
- ISO/IEC 42001
- ISO/IEC 27001
- LGPD
- PIPEDA
- PIPL
- PDPA
- APPI
- UAE PDPL
- Saudi PDPL
- NDPA
- POPIA
We don’t stop at advice. We get you compliant.
For Indian and global companies, from startups to enterprises, and for the investors who back them.
Compliance implementation, done with you
We do the work, not just the advice: privacy notices, consent flows, records of processing, DPIAs and AI impact assessments, vendor terms, policies and staff training, built with your team until you are compliant.
Tell us what you need- Privacy notices and consent flowsWritten for your product and every market it reaches.
- Data maps and records of processingWhat you collect, where it goes, and on what basis.
- DPIAs and AI impact assessmentsFor the processing and the AI systems that need them.
- AI governance frameworkPolicy, AI inventory and risk register, mapped to the EU AI Act and ISO/IEC 42001.
- Incident-response playbooksWho reports what, to whom, within CERT-In’s six hours, the GDPR’s 72 or NIS2’s 24.
- Vendor and customer termsData processing agreements, transfer clauses and security schedules.
- Policies and staff trainingShort, practical, and specific to how your team works.
- Kept currentA monthly check of what changed in your markets and what to do about it.
DPDP readiness pack for companies serving users in India
Whether the Act applies to you, a cited gap analysis of what has to change, and a plan ordered by the dates each duty starts.
Usually about 7 working daysEU AI Act readiness assessment
Which of your AI systems the Act covers, the risk class of each, and the obligations and deadlines that follow from it.
Usually about 10 working daysISO/IEC 42001 gap assessment
Your AI management practices measured against ISO/IEC 42001, with the gaps to close before a certification audit.
Usually about 12 working daysMonthly regulatory monitoring
A short monthly note on new rules, guidance and enforcement that affect you, with what to do about each.
Monthly, cancel any timePrivacy readiness across your markets
Which privacy laws apply in each country you serve, what they require of you, and one plan that satisfies them together.
Usually about 12 working daysAI governance programme
An inventory of your AI systems mapped to the EU AI Act, NIST AI RMF, ISO/IEC 42001 and national AI laws, with the controls to put in place.
Usually about 15 working daysPrivacy and AI due diligence for investors
A cited review of a target company's privacy and AI compliance across its markets, with the risks that matter to the deal.
Usually about 7 working daysCybersecurity compliance and incident readiness
Which cyber laws bind you (NIS2, the Cyber Resilience Act, DORA, CERT-In, SEC and state rules and others), then the policies, incident-response plan and reporting playbooks they require, written for your team.
Usually about 12 working daysWe are a compliance practice: we assess, implement and keep you current. Where a question needs a formal legal opinion, we say so.
How an engagement works
Tell us about your product
What it does, what personal data or AI it involves, and where your users are.
Get a fixed quote
We confirm which rules apply and send a scope and price before anything starts.
We assess
Each requirement is cited to the official text and checked three times, then reviewed and approved by our lead human advisors.
We implement
We draft the documents, set up the processes and train your people, working alongside your team.
We keep you current
As the rules change in your markets, we tell you what it means and update what we built.
The clock is already running
The dates we plan your work around. Updated as the rules change; every date links to the official source.
Where the rules are moving
Tap a place to see what applies there
United States
What we cover
- California CCPA/CPRA and its regulations
- Other state privacy laws
- Colorado's AI law (SB 26-189)
- NIST AI RMF
- FTC Act section 5
- SEC cyber disclosure rules
- NYDFS Part 500
- State breach notification laws
Key dates
- in 2 months
California's CCPA rules on automated decision-making technology apply
cppa.ca.gov ↗ - in 2 months
Colorado's AI law (SB 26-189, which replaced the 2024 AI Act) takes effect
leg.colorado.gov ↗ - in 14 months
California CCPA risk assessments must be completed
cppa.ca.gov ↗ - in 17 months
First California cybersecurity audit certifications due (businesses over $100 million revenue)
cppa.ca.gov ↗
Canada
What we cover
- PIPEDA
- Quebec's Law 25
- CASL
No dated deadline on our list right now. We track changes here every week.
Ask about Canada →Mexico
What we cover
- LFPDPPP
No dated deadline on our list right now. We track changes here every week.
Ask about Mexico →Brazil
What we cover
- LGPD
No dated deadline on our list right now. We track changes here every week.
Ask about Brazil →Chile
What we cover
- Law 21.719 (new data protection law)
Key dates
- in 21 days
Chile's new data protection law (Law 21.719) takes effect; a bill to postpone it is before the Senate
bcn.cl ↗
United Kingdom
What we cover
- UK GDPR and Data Protection Act 2018
- Data (Use and Access) Act 2025
- PECR
- NIS Regulations and the Cyber Security and Resilience Bill
No dated deadline on our list right now. We track changes here every week.
Ask about United Kingdom →European Union
What we cover
- GDPR
- EU AI Act
- ePrivacy Directive
- Data Act
- NIS2
- Cyber Resilience Act
- DORA
Key dates
- In force
EU AI Act transparency duties (Article 50) apply
eur-lex.europa.eu ↗ - In force
EU Cyber Resilience Act: manufacturers must report actively exploited vulnerabilities and severe incidents (Article 14)
eur-lex.europa.eu ↗ - in 13 months
EU AI Act high-risk duties for Annex III systems, as amended by Regulation (EU) 2026/1744
eur-lex.europa.eu ↗ - in 13 months
EU Cyber Resilience Act applies in full: security requirements for hardware and software products sold in the EU
eur-lex.europa.eu ↗ - in 21 months
EU AI Act high-risk duties for AI in products covered by EU product law
eur-lex.europa.eu ↗
Nigeria
What we cover
- Nigeria Data Protection Act 2023
- Cybercrimes Act (amended 2024)
No dated deadline on our list right now. We track changes here every week.
Ask about Nigeria →Kenya
What we cover
- Data Protection Act 2019
- Computer Misuse and Cybercrimes Act 2018
No dated deadline on our list right now. We track changes here every week.
Ask about Kenya →South Africa
What we cover
- POPIA
- Cybercrimes Act 2020
No dated deadline on our list right now. We track changes here every week.
Ask about South Africa →Gulf states
What we cover
- UAE PDPL
- DIFC and ADGM data protection
- Saudi PDPL
- Qatar's PDPPL
- Bahrain's and Oman's PDPLs
- UAE cybercrime law
- Saudi NCA cybersecurity controls
No dated deadline on our list right now. We track changes here every week.
Ask about Gulf states →India
What we cover
- DPDP Act, 2023 and DPDP Rules, 2025
- IT Act, 2000
- CERT-In six-hour incident reporting
- RBI and SEBI cyber frameworks
Key dates
- In force
DPDP Rules notified; Data Protection Board provisions in force
meity.gov.in ↗ - in 3 days
Consent managers can register with the Data Protection Board
meity.gov.in ↗ - in 6 months
Most DPDP duties apply: notice, consent, security, breach reporting, rights
meity.gov.in ↗
China
What we cover
- PIPL
- Cybersecurity Law (amended 2026)
- Data Security Law
- AI measures
No dated deadline on our list right now. We track changes here every week.
Ask about China →South Korea
What we cover
- PIPA
- AI Basic Act
No dated deadline on our list right now. We track changes here every week.
Ask about South Korea →Japan
What we cover
- APPI
- Active Cyber Defence Act
No dated deadline on our list right now. We track changes here every week.
Ask about Japan →South-East Asia
What we cover
- Singapore's PDPA
- Malaysia's PDPA
- Thailand's PDPA
- Philippines' Data Privacy Act
- Indonesia's PDP Law
- Vietnam's PDPD
- Singapore's Cybersecurity Act
No dated deadline on our list right now. We track changes here every week.
Ask about South-East Asia →Australia
What we cover
- Privacy Act 1988 and the Australian Privacy Principles
- Cyber Security Act 2024 (ransomware payment reporting)
- SOCI Act
Key dates
- in 30 days
Privacy policies must explain automated decisions that significantly affect people (APPs 1.7 and 1.8)
oaic.gov.au ↗
Standards (worldwide)
What we cover
- ISO/IEC 42001 (AI management)
- ISO/IEC 27001 and 27701
- NIST CSF 2.0
- NIST AI RMF
- SOC 2
- Budapest Convention
No dated deadline on our list right now. We track changes here every week.
Ask about Standards (worldwide) →See all dates as a list
Where today sits
3 of 14 dates have passed
- 1 earlier date already in force
- EUIn force
EU Cyber Resilience Act: manufacturers must report actively exploited vulnerabilities and severe incidents (Article 14)
Source: EUR-Lex ↗ - Today
- Chilein 21 days
Chile's new data protection law (Law 21.719) takes effect; a bill to postpone it is before the Senate
Source: BCN Chile ↗ - Australiain 30 days
Privacy policies must explain automated decisions that significantly affect people (APPs 1.7 and 1.8)
Source: OAIC ↗ - United Statesin 2 months
California's CCPA rules on automated decision-making technology apply
Source: California Privacy Protection Agency ↗ - United Statesin 2 months
Colorado's AI law (SB 26-189, which replaced the 2024 AI Act) takes effect
Source: Colorado General Assembly ↗ - Indiain 6 months
Most DPDP duties apply: notice, consent, security, breach reporting, rights
Source: MeitY ↗ Show 5 later datesHide later dates
- EUin 13 months
EU AI Act high-risk duties for Annex III systems, as amended by Regulation (EU) 2026/1744
Source: EUR-Lex ↗ - EUin 13 months
EU Cyber Resilience Act applies in full: security requirements for hardware and software products sold in the EU
Source: EUR-Lex ↗ - United Statesin 14 months
California CCPA risk assessments must be completed
Source: California Privacy Protection Agency ↗ - United Statesin 17 months
First California cybersecurity audit certifications due (businesses over $100 million revenue)
Source: California Privacy Protection Agency ↗ - EUin 21 months
EU AI Act high-risk duties for AI in products covered by EU product law
Source: EUR-Lex ↗
Consent managers can register with the Data Protection Board
3 days
- 1 DecChile New data protection law (Law 21.719) takes effect; a bill to postpone it is before the Senate21d
- 10 DecAustralia Privacy policies must explain automated decisions that significantly affect people (APPs 1.7 and 1.8)30d
- 1 JanUnited States California's CCPA rules on automated decision-making technology apply52d
Why Agent L exists
Compliance advice has a familiar shape. A long engagement letter, a team you never meet, a hundred-page report that arrives after the deadline it was meant to prepare you for, and an invoice nobody could have predicted. A company selling across borders has three simple questions for every market it enters: does this law apply to us, what has to change, and by when. They rarely get simple answers.
Meanwhile the rules multiply and move. India is phasing in its DPDP Rules, the EU amended its AI Act before the main duties began, US states keep adding privacy and AI laws, cyber incident-reporting rules keep tightening, from India's six-hour window to the EU's Cyber Resilience Act, and new regimes are arriving across Latin America, Asia-Pacific, the Gulf and Africa. Advice that was right in spring can be out of date by autumn, and most companies find out only when a customer's security questionnaire, an investor's due diligence or a regulator asks.
We think compliance work should feel like good engineering: precise, traceable and on time. So we built a practice that works the way the best software teams do. AI agents research, draft and cross-check around the clock. Every legal statement is tied to the official text it comes from, and checked against it three times. Then we do the work with your team: the notices, the processes, the playbooks and the training, until the gaps are closed. And our lead human advisors read and sign off every deliverable before it reaches you.
Our aim is simple to say and hard to do: any company, from a five-person startup to a multinational, and the investors who back them, should understand their obligations in every market they serve as clearly as if they had a legal team in each, with the cost agreed up front and early enough to act. Clear answers, cited sources, and one plan in the order the dates demand. That is the whole idea behind Agent L.
In plain terms: our AI assistants prepare routine emails and say so when they send them. Every assessment, report, quote and invoice is reviewed and approved by our lead human advisors before it reaches you.
Recent insights
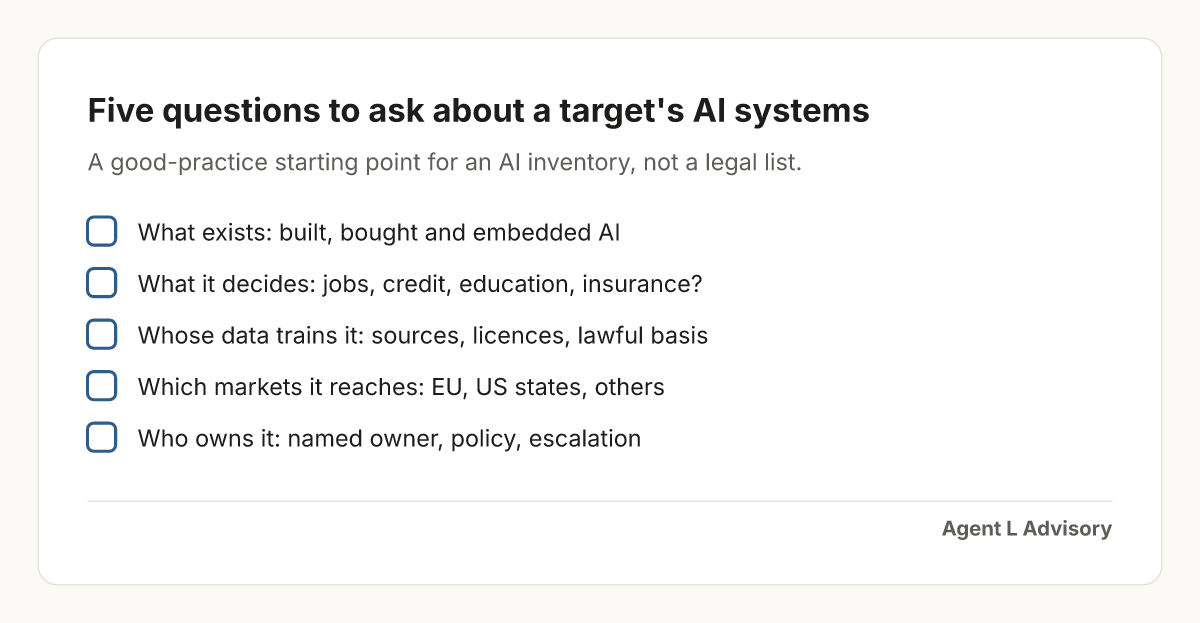 AI due diligence: five questions to ask about a target
AI due diligence: five questions investors can ask about a target's AI systems, training data, markets and internal ownership.
 Cyber Resilience Act reporting: the 24-hour and 72-hour rules
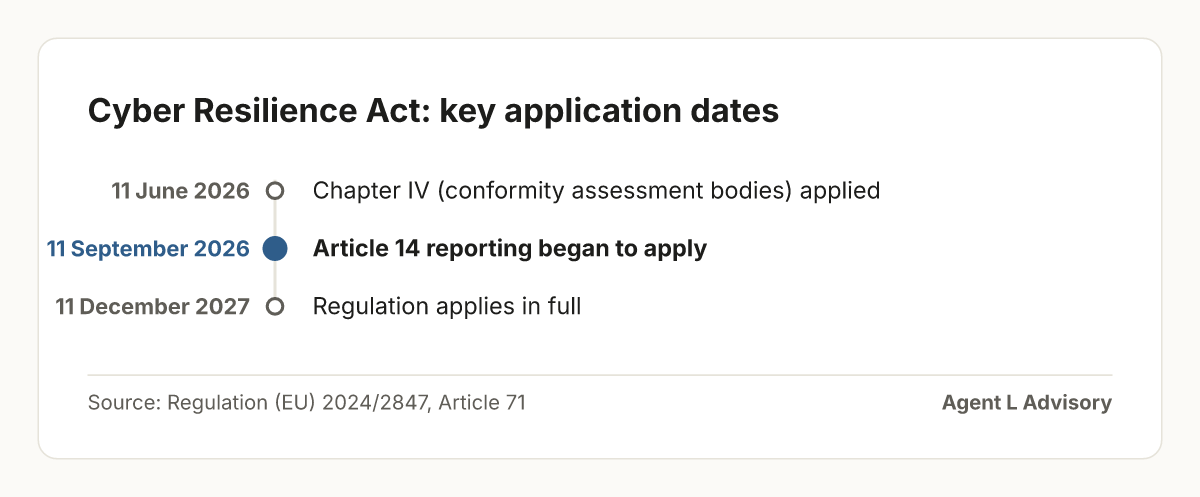
Cyber Resilience Act reporting: who must report, the 24-hour and 72-hour deadlines under Article 14, where reports go, and how it differs from NIS2.
 Can a Company Be a DPDP Consent Manager? Who Can Register
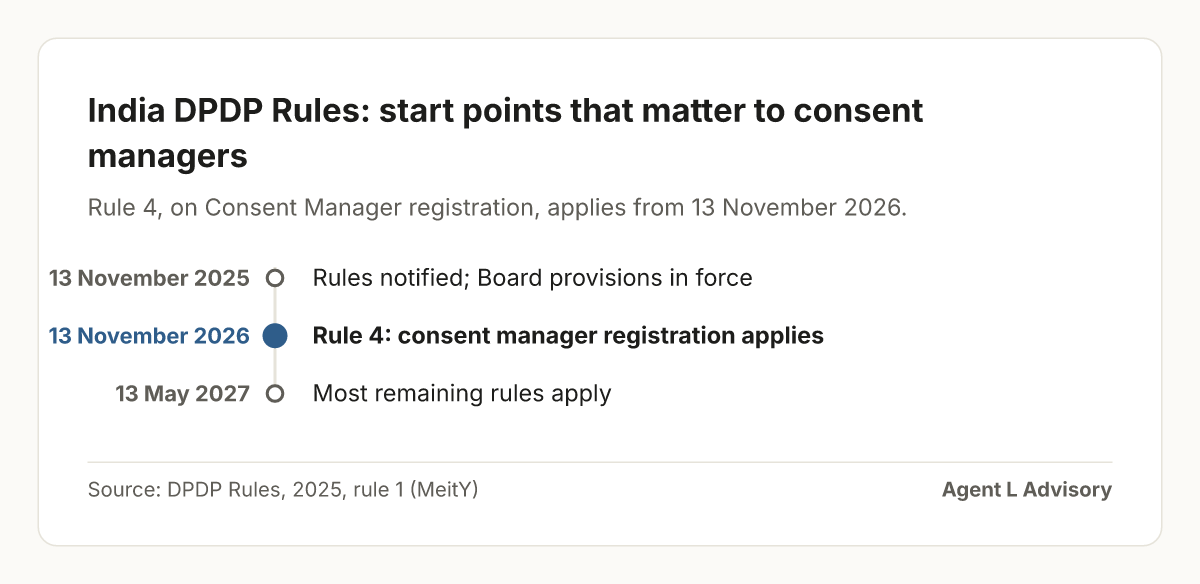
Can a company be a DPDP consent manager? What the Act and Rules say about who can register, and when rule 4 registration applies.
Good to know
Can we start small?
Yes. Ask for a free readiness snapshot: two pages on which privacy, AI and cyber laws apply to your company, the dates that matter, and the gaps we can see from your public pages, reviewed by our lead human advisors. There is no obligation, and we need nothing from you to prepare it.
Do you only advise, or do you do the work?
We do the work. After the assessment we draft your notices, policies, assessments, contracts and incident playbooks, set up the processes with your team and train your people, and we can keep it all current every month. This is compliance work rather than a legal opinion; where a question needs a formal opinion, we tell you.
Who does the work?
The research and drafting is done by AI agents, openly. Every regulatory claim is cited to the official text and checked three times: for facts, for citations against the source, and by an adversarial expert review. Our lead human advisors then review and approve every report before it reaches you.
Which laws and countries do you cover?
Privacy, data-protection, AI and cybersecurity laws across India, the EU and UK, the United States and Canada, Asia-Pacific, the Middle East, Africa and Latin America, from the DPDP Act and CERT-In directions to the GDPR, NIS2, DORA and the Cyber Resilience Act, plus ISO/IEC 42001, ISO/IEC 27001 and the NIST frameworks. Each requirement is cited to the official text of the law it comes from.
Which companies is this for?
Indian companies preparing for the DPDP Rules and CERT-In reporting, startups expanding into new markets, mid-size companies and enterprises in data-heavy or regulated sectors, investors who need privacy, AI and cyber due diligence, and firms that want a specialist alongside them for their clients.
How is the fee set?
You get a fixed quote with the scope before any work starts. Nothing is charged that was not in the quote you accepted.
What happens to what I send through this site?
Only what you type in the form is collected, and only to answer you. This site sets no cookies and loads nothing from third parties. The privacy notice explains who processes it and your rights.
Ask a question
Tell us what you are building and where your users are. You will get a plain answer by email, or write to hello@agentl.in.
- Usually a reply within one working day
- A fixed quote before any work starts
- Only what you type here is collected